

DumpsKing FCSS_SASE_AD-25 Real Exam Question Answers Updated [Oct 20, 2025]
Easily To Pass New Fortinet FCSS_SASE_AD-25 Dumps with 56 Questions
NEW QUESTION # 10
For a SASE deployment, what is a crucial step when configuring security checks for regulatory compliance?
- A. Manual verification by external auditors
- B. Continuous monitoring and automatic updates of compliance rules
- C. Annual reviews of compliance status
- D. Periodic rollback of security updates
Answer: B
NEW QUESTION # 11
Which FortiOS command is used to verify the health of Zero Trust Network Access (ZTNA) policies in FortiSASE?
- A. diagnose debug application ztna
- B. get system ztna status
- C. diagnose ztna status
- D. get ztna policy-status
Answer: A
NEW QUESTION # 12
Refer to the exhibits.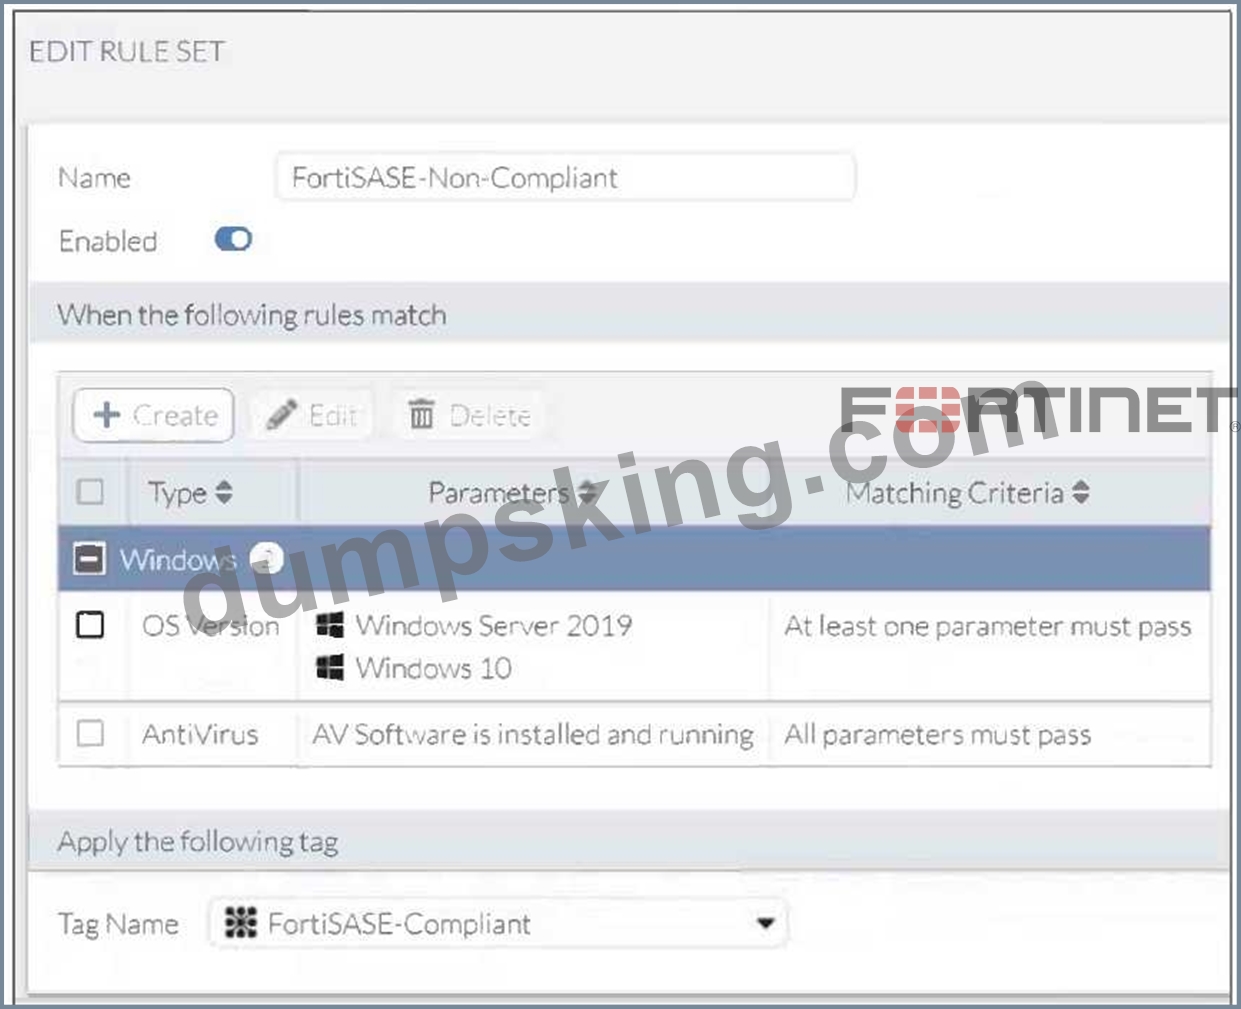
Antivirus is installed on a Windows 10 endpoint, but the windows application firewall is stopping it from running. What will the endpoint security posture check be?
- A. FortiClient will tag the endpoint as FortiSASE-Non-Compliant.
- B. FortiClient will prompt the user to enable antivirus.
- C. FortiClient telemetry will be disconnected because of failed compliance.
- D. FortiClient will block the endpoint from getting access to the network.
Answer: D
NEW QUESTION # 13
Which event log subtype captures FortiSASE SSL VPN user creation?
- A. Endpoint Events
- B. Administrator Events
- C. VPN Events
- D. User Events
Answer: D
Explanation:
The event log subtype that captures FortiSASE SSL VPN user creation is User Events . This subtype is specifically designed to log activities related to user management, such as creating, modifying, or deleting user accounts. When an SSL VPN user is created, it falls under this category because it involves adding a new user to the system.
Here's why the other options are incorrect:
A . Endpoint Events: These logs pertain to activities related to endpoint devices, such as device registration, compliance checks, or security posture assessments. SSL VPN user creation is unrelated to endpoint events.
B . VPN Events: These logs capture activities related to VPN connections, such as session establishment, termination, or errors. While SSL VPN usage generates VPN events, the creation of a user account itself is not logged under this subtype.
D . Administrator Events: These logs track actions performed by administrators, such as configuration changes or policy updates. While an administrator might create the SSL VPN user, the specific event of user creation is categorized under User Events, not Administrator Events.
Fortinet FCSS FortiSASE Documentation - Event Logging and Subtypes
FortiSASE Administration Guide - Monitoring and Logging
NEW QUESTION # 14
What are two advantages of using zero-trust tags? (Choose two.)
- A. Zero-trust tags can be used to allow or deny access to network resources
- B. Zero-trust tags can determine the security posture of an endpoint.
- C. Zero-trust tags can be used to create multiple endpoint profiles which can be applied to different endpoints
- D. Zero-trust tags can be used to allow secure web gateway (SWG) access
Answer: A,B
Explanation:
Zero-trust tags are critical in implementing zero-trust network access (ZTNA) policies. Here are the two key advantages of using zero-trust tags:
Access Control (Allow or Deny):
Zero-trust tags can be used to define policies that either allow or deny access to specific network resources based on the tag associated with the user or device.
This granular control ensures that only authorized users or devices with the appropriate tags can access sensitive resources, thereby enhancing security.
Determining Security Posture:
Zero-trust tags can be utilized to assess and determine the security posture of an endpoint.
Based on the assigned tags, FortiSASE can evaluate the device's compliance with security policies, such as antivirus status, patch levels, and configuration settings.
Devices that do not meet the required security posture can be restricted from accessing the network or given limited access.
FortiOS 7.2 Administration Guide: Provides detailed information on configuring and using zero-trust tags for access control and security posture assessment.
FortiSASE 23.2 Documentation: Explains how zero-trust tags are implemented and used within the FortiSASE environment for enhancing security and compliance.
NEW QUESTION # 15
When viewing the daily summary report generated by FortiSASE, the administrator notices that the report contains very little data.
What is a possible explanation for this almost empty report?
- A. Digital experience monitoring is not configured.
- B. There are no security profile groups applied to all policies.
- C. The web filter security profile is not set to Monitor.
- D. Log allowed traffic is set to Security Events for all policies.
Answer: D
Explanation:
The issue of an almost empty daily summary report in FortiSASE can often be traced back to how logging is configured within the system. Specifically, if "Log Allowed Traffic" is set to "Security Events" for all policies, it means that only security-related events (such as threats or anomalies) are being logged, while normal, allowed traffic is not being recorded. Since most traffic in a typical network environment is allowed, this configuration would result in very little data being captured and subsequently reported in the daily summary.
Here's a breakdown of why the other options are less likely to be the cause:
B . There are no security profile groups applied to all policies: While applying security profiles is important for comprehensive protection, their absence does not directly affect the volume of data in reports unless specific logging settings are also misconfigured.
C . The web filter security profile is not set to Monitor: This option pertains specifically to web filtering activities. Even if web filtering is not set to monitor mode, other types of traffic and logs should still populate the report.
D . Digital experience monitoring is not configured: Digital Experience Monitoring (DEM) focuses on user experience metrics rather than general traffic logging. Its absence would not lead to an almost empty report.
To resolve this issue, administrators should review the logging settings across all policies and ensure that "Log Allowed Traffic" is appropriately configured to capture the necessary data for reporting purposes.
Fortinet FCSS FortiSASE Documentation - Reporting and Logging Best Practices FortiSASE Administration Guide - Configuring Logging Settings
NEW QUESTION # 16
Which statement applies to a single sign-on (SSO) deployment on FortiSASE?
- A. SSO identity providers can be integrated using public and private access types.
- B. SSO is recommended only for agent-based deployments.
- C. SSO overrides any other previously configured user authentication.
- D. SSO users can be imported into FortiSASE and added to user groups.
Answer: C
NEW QUESTION # 17
Refer to the exhibit.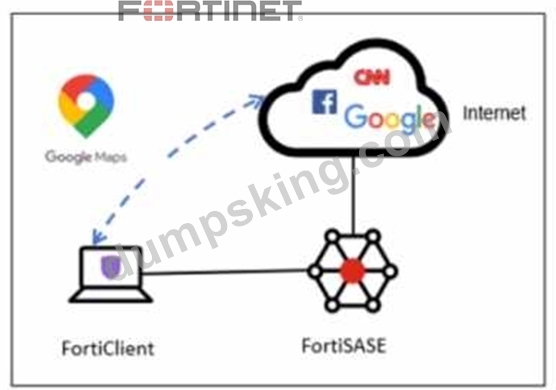
A company has a requirement to inspect all the endpoint internet traffic on FortiSASE, and exclude Google Maps traffic from the FortiSASE VPN tunnel and redirect it to the endpoint physical Interface. Which configuration must you apply to achieve this requirement?
- A. Exempt the Google Maps FQDN from the endpoint system proxy settings.
- B. Configure the Google Maps FQDN as a split tunneling destination on the FortiSASE endpoint profile.
- C. Change the default DNS server configuration on FortiSASE to use the endpoint system DNS.
- D. Configure a static route with the Google Maps FQDN on the endpoint to redirect traffic
Answer: B
Explanation:
To meet the requirement of inspecting all endpoint internet traffic on FortiSASE while excluding Google Maps traffic from the FortiSASE VPN tunnel and redirecting it to the endpoint's physical interface, you should configure split tunneling. Split tunneling allows specific traffic to bypass the VPN tunnel and be routed directly through the endpoint's local interface.
Split Tunneling Configuration:
Split tunneling enables selective traffic to be routed outside the VPN tunnel.
By configuring the Google Maps Fully Qualified Domain Name (FQDN) as a split tunneling destination, you ensure that traffic to Google Maps bypasses the VPN tunnel and uses the endpoint's local interface instead.
Implementation Steps:
Access the FortiSASE endpoint profile configuration.
Add the Google Maps FQDN to the split tunneling destinations list.
This configuration directs traffic intended for Google Maps to bypass the VPN tunnel and be routed directly through the endpoint's physical network interface.
FortiOS 7.2 Administration Guide: Provides details on split tunneling configuration.
FortiSASE 23.2 Documentation: Explains how to set up and manage split tunneling for specific destinations.
NEW QUESTION # 18
A customer wants to upgrade their legacy on-premises proxy to a could-based proxy for a hybrid network. Which FortiSASE features would help the customer to achieve this outcome?
- A. SD-WAN and NGFW
- B. secure web gateway (SWG) and inline-CASB
- C. zero trust network access (ZTNA) and next generation firewall (NGFW)
- D. SD-WAN and inline-CASB
Answer: B
Explanation:
For a customer looking to upgrade their legacy on-premises proxy to a cloud-based proxy for a hybrid network, the combination of Secure Web Gateway (SWG) and Inline Cloud Access Security Broker (CASB) features in FortiSASE will provide the necessary capabilities.
Secure Web Gateway (SWG):
SWG provides comprehensive web security by inspecting and filtering web traffic to protect against web-based threats.
It ensures that all web traffic, whether originating from on-premises or remote locations, is inspected and secured by the cloud-based proxy.
Inline Cloud Access Security Broker (CASB):
CASB enhances security by providing visibility and control over cloud applications and services.
Inline CASB integrates with SWG to enforce security policies for cloud application usage, preventing unauthorized access and data leakage.
FortiOS 7.2 Administration Guide: Details on SWG and CASB features.
FortiSASE 23.2 Documentation: Explains how SWG and inline-CASB are used in cloud-based proxy solutions.
NEW QUESTION # 19
Refer to the exhibits.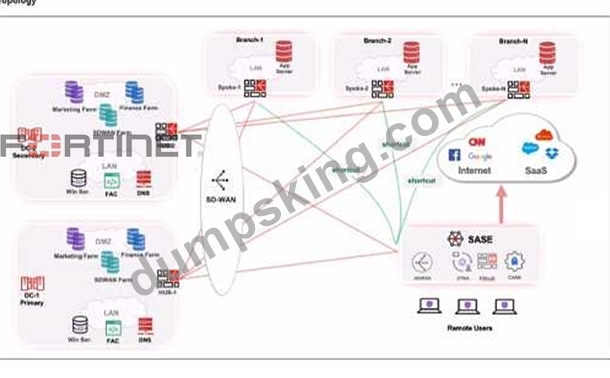
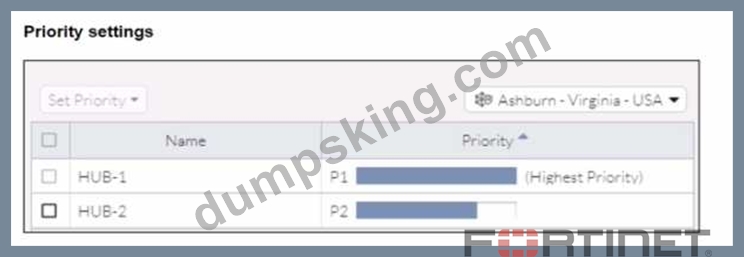
When remote users connected to FortiSASE require access to internal resources on Branch-2. how will traffic be routed?
- A. FortiSASE will use the SD-WAN capability and determine that traffic will be directed to HUB-2. which will then route traffic to Branch-2.
- B. FortiSASE will use the SD-WAN capability and determine that traffic will be directed to HUB-1, which will then route traffic to Branch-2.
- C. FortiSASE will use the AD VPN protocol and determine that traffic will be directed to Branch-2 directly, using a dynamic route
- D. FortiSASE will use the AD VPN protocol and determine that traffic will be directed to Branch-2 directly, using a static route
Answer: C
NEW QUESTION # 20
What key components are involved in Secure Internet Access (SIA) within FortiSASE?
(Select all that apply)
- A. Malware protection
- B. Content filtering
- C. Web application firewall (WAF)
- D. Bandwidth throttling
Answer: A,B,C
NEW QUESTION # 21
When viewing the daily summary report generated by FortiSASE, the administrator notices that the report contains very little data.
What is a possible explanation for this almost empty report?
- A. Digital experience monitoring is not configured.
- B. There are no security profile groups applied to all policies.
- C. The web filter security profile is not set to Monitor.
- D. Log allowed traffic is set to Security Events for all policies.
Answer: D
Explanation:
The issue of an almost empty daily summary report in FortiSASE can often be traced back to how logging is configured within the system. Specifically, if "Log Allowed Traffic" is set to "Security Events" for all policies, it means that only security-related events (such as threats or anomalies) are being logged, while normal, allowed traffic is not being recorded. Since most traffic in a typical network environment is allowed, this configuration would result in very little data being captured and subsequently reported in the daily summary.
Here's a breakdown of why the other options are less likely to be the cause:
B . There are no security profile groups applied to all policies: While applying security profiles is important for comprehensive protection, their absence does not directly affect the volume of data in reports unless specific logging settings are also misconfigured.
C . The web filter security profile is not set to Monitor: This option pertains specifically to web filtering activities. Even if web filtering is not set to monitor mode, other types of traffic and logs should still populate the report.
D . Digital experience monitoring is not configured: Digital Experience Monitoring (DEM) focuses on user experience metrics rather than general traffic logging. Its absence would not lead to an almost empty report.
To resolve this issue, administrators should review the logging settings across all policies and ensure that "Log Allowed Traffic" is appropriately configured to capture the necessary data for reporting purposes.
Fortinet FCSS FortiSASE Documentation - Reporting and Logging Best Practices FortiSASE Administration Guide - Configuring Logging Settings
NEW QUESTION # 22
You are designing a new network for Company X and one of the new cybersecurity policy requirements is that all remote user endpoints must always be connected and protected Which FortiSASE component facilitates this always-on security measure?
- A. site-based deployment
- B. thin-branch SASE extension
- C. unified FortiClient
- D. inline-CASB
Answer: C
Explanation:
The unified FortiClient component of FortiSASE facilitates the always-on security measure required for ensuring that all remote user endpoints are always connected and protected.
Unified FortiClient:
FortiClient is a comprehensive endpoint security solution that integrates with FortiSASE to provide continuous protection for remote user endpoints.
It ensures that endpoints are always connected to the FortiSASE infrastructure, even when users are off the corporate network.
Always-On Security:
The unified FortiClient maintains a persistent connection to FortiSASE, enforcing security policies and protecting endpoints against threats at all times.
This ensures compliance with the cybersecurity policy requiring constant connectivity and protection for remote users.
FortiOS 7.2 Administration Guide: Provides information on configuring and managing FortiClient for endpoint security.
FortiSASE 23.2 Documentation: Explains how FortiClient integrates with FortiSASE to deliver always-on security for remote endpoints.
NEW QUESTION # 23
Refer to the exhibits.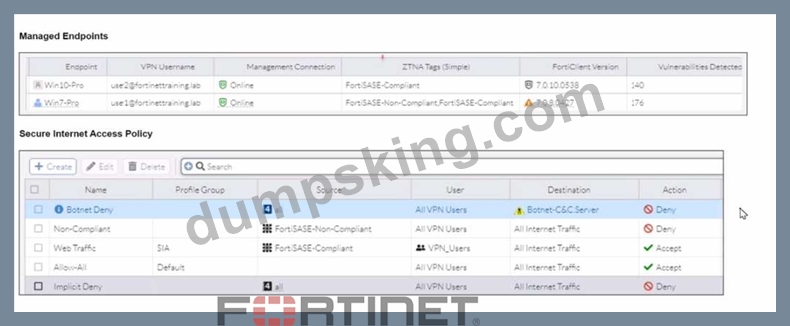
WiMO-Pro and Win7-Pro are endpoints from the same remote location. WiMO-Pro can access the internet though FortiSASE, while Wm7-Pro can no longer access the internet Given the exhibits, which reason explains the outage on Wm7-Pro?
- A. The Win7-Pro FortiClient version does not match the FortiSASE endpoint requirement.
- B. The Win7-Pro device posture has changed.
- C. Win-7 Pro has exceeded the total vulnerability detected threshold.
- D. Win7-Pro cannot reach the FortiSASE SSL VPN gateway
Answer: C
Explanation:
Based on the provided exhibits, the reason why the Win7-Pro endpoint can no longer access the internet through FortiSASE is due to exceeding the total vulnerability detected threshold. This threshold is used to determine if a device is compliant with the security requirements to access the network.
Endpoint Compliance:
FortiSASE monitors endpoint compliance by assessing various security parameters, including the number of vulnerabilities detected on the device.
The compliance status is indicated by the ZTNA tags and the vulnerabilities detected.
Vulnerability Threshold:
The exhibit shows that Win7-Pro has 176 vulnerabilities detected, whereas Win10-Pro has 140 vulnerabilities.
If the endpoint exceeds a predefined vulnerability threshold, it may be restricted from accessing the network to ensure overall network security.
Impact on Network Access:
Since Win7-Pro has exceeded the vulnerability threshold, it is marked as non-compliant and subsequently loses internet access through FortiSASE.
The FortiSASE endpoint profile enforces this compliance check to prevent potentially vulnerable devices from accessing the internet.
FortiOS 7.2 Administration Guide: Provides information on endpoint compliance and vulnerability management.
FortiSASE 23.2 Documentation: Explains how vulnerability thresholds are used to determine endpoint compliance and access control.
NEW QUESTION # 24
Which feature should be prioritized when configuring dashboards in FortiSASE for monitoring network traffic?
- A. Real-time traffic flow
- B. User access logs
- C. Historical bandwidth usage
- D. Comparative analysis of past and present data
Answer: A
NEW QUESTION # 25
During FortiSASE provisioning, how many security points of presence (POPs) need to be configured by the FortiSASE administrator?
- A. 0
- B. 1
- C. 2
- D. 3
Answer: D
NEW QUESTION # 26
Which two deployment methods are used to connect a FortiExtender as a FortiSASE LAN extension? (Choose two.)
- A. Connect FortiExtender to FortiSASE using FortiZTP
- B. Enable Control and Provisioning Wireless Access Points (CAPWAP) access on the FortiSASE portal.
- C. Configure an IPsec tunnel on FortiSASE to connect to FortiExtender.
- D. Enter the FortiSASE domain name in the FortiExtender GUI as a static discovery server
Answer: A,D
Explanation:
There are two deployment methods used to connect a FortiExtender as a FortiSASE LAN extension:
Connect FortiExtender to FortiSASE using FortiZTP:
FortiZero Touch Provisioning (FortiZTP) simplifies the deployment process by allowing FortiExtender to automatically connect and configure itself with FortiSASE.
This method requires minimal manual configuration, making it efficient for large-scale deployments.
Enter the FortiSASE domain name in the FortiExtender GUI as a static discovery server:
Manually configuring the FortiSASE domain name in the FortiExtender GUI allows the extender to discover and connect to the FortiSASE infrastructure.
This static discovery method ensures that FortiExtender can establish a connection with FortiSASE using the provided domain name.
FortiOS 7.2 Administration Guide: Details on FortiExtender deployment methods and configurations.
FortiSASE 23.2 Documentation: Explains how to connect and configure FortiExtender with FortiSASE using FortiZTP and static discovery.
NEW QUESTION # 27
Which role does FortiSASE play in supporting zero trust network access (ZTNA) principles9
- A. It can identify attributes on the endpoint for security posture check.
- B. It enables VPN connections for remote employees.
- C. It integrates with software-defined network (SDN) solutions.
- D. It offers hardware-based firewalls for network segmentation.
Answer: A
Explanation:
FortiSASE supports zero trust network access (ZTNA) principles by identifying attributes on the endpoint for security posture checks. ZTNA principles require continuous verification of user and device credentials, as well as their security posture, before granting access to network resources.
Security Posture Check:
FortiSASE can evaluate the security posture of endpoints by checking for compliance with security policies, such as antivirus status, patch levels, and configuration settings.
This ensures that only compliant and secure devices are granted access to the network.
Zero Trust Network Access (ZTNA):
ZTNA is based on the principle of "never trust, always verify," which requires continuous assessment of user and device trustworthiness.
FortiSASE plays a crucial role in implementing ZTNA by performing these security posture checks and enforcing access control policies.
FortiOS 7.2 Administration Guide: Provides information on ZTNA and endpoint security posture checks.
FortiSASE 23.2 Documentation: Details on how FortiSASE implements ZTNA principles.
NEW QUESTION # 28
Which policy type is used to control traffic between the FortiClient endpoint to FortiSASE for secure internet access?
- A. VPN policy
- B. secure web gateway (SWG) policy
- C. thin edge policy
- D. private access policy
Answer: A
NEW QUESTION # 29
How does FortiSASE hide user information when viewing and analyzing logs?
- A. By encrypting data using Secure Hash Algorithm 256-bit (SHA-256)
- B. By hashing data using salt
- C. By encrypting data using advanced encryption standard (AES)
- D. By hashing data using Blowfish
Answer: B
Explanation:
FortiSASE hides user information when viewing and analyzing logs by hashing data using salt. This approach ensures that sensitive user information is obfuscated, enhancing privacy and security.
Hashing Data with Salt:
Hashing data involves converting it into a fixed-size string of characters, which is typically a hash value.
Salting adds random data to the input of the hash function, ensuring that even identical inputs produce different hash values.
This method provides enhanced security by making it more difficult to reverse-engineer the original data from the hash value.
Security and Privacy:
Using salted hashes ensures that user information remains secure and private when stored or analyzed in logs.
This technique is widely used in security systems to protect sensitive data from unauthorized access.
FortiOS 7.2 Administration Guide: Provides information on log management and data protection techniques.
FortiSASE 23.2 Documentation: Details on how FortiSASE implements data hashing and salting to secure user information in logs.
NEW QUESTION # 30
......
Latest FCSS_SASE_AD-25 Study Guides 2025 - With Test Engine PDF: https://dumpstorrent.dumpsking.com/FCSS_SASE_AD-25-testking-dumps.html
